"The most toxic and dangerous type of radioactive waste created by the nuclear industry"
This is waste generated by nuclear power plants called 'high-level radioactive waste' (HLW), also known as 'spent' or 'irradiated' fuel. This waste contains plutonium, uranium, strontium, and cesium; and will be radioactive for millions of years.
It is not like the waste currently stored at the Waste Isolation Pilot Project (WIPP) or any other waste site that exists today in the U.S.: it is far worse.
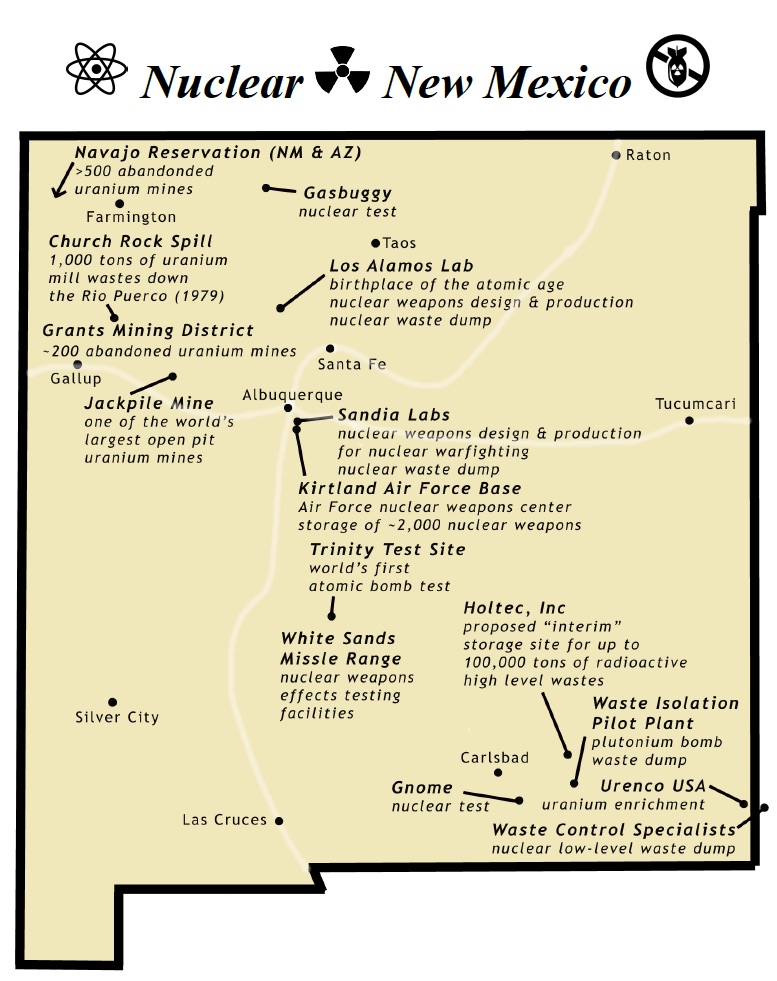
Two companies are proposing to build waste facilities near Carlsbad and Hobbs for the most toxic and dangerous type of radioactive waste created by the nuclear industry.
Holtec International is working with the Eddy-Lea Energy Alliance, LLC (ELEA) to apply for a license to build a Consolidated Interim Storage (CIS) facility approximately halfway between Carlsbad and Hobbs, and 16 miles north of WIPP.
The Nuclear Regulatory Commission (NRC) has declared the Holtec/ELEA application complete, NRC initiated a public comment period with 60 days for public comment. Note that transport of this waste poses risks to the environment and all life located near transportation routes.
Holtec proposal:
New CIS facility to store 100,000 metric tons of HLRW, with the potential to increase to 120,000 metric tons for 120 years
Shallow sub-surface burial system
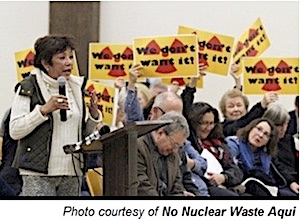
New Mexicans and Texans are fighting the attempted licensing of these two proposed CIS facilities - Waste Control Specialists near Andrews, Texas and Eddy Lee/Holtec International east of Carlsbad, New Mexico.
These sites and any transport to these sites are not only dangerous but environmentally unjust. These sites present clear examples of environmental racism.
New Mexico's demographic is largely Latino. There are many communities of color, especially in the southern part of the state where the sites are being proposed. People of color would be disproportionately affected if the Eddy Lee/Holtec CIS site were licensed and constructed.
New Mexico and Texas do not consent to either proposed CIS facility and are fighting to avoid the environmental injustice and the unnecessary shipment of irradiated high-level nuclear waste through their communities.
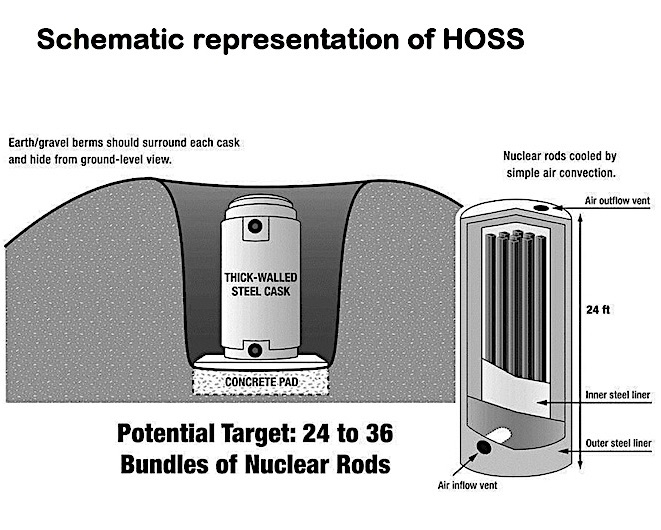
Hardened On-Site Storage (HOSS) is a community-based concept that aims to protect the public from the threats posed by the current vulnerable storage of commercial irradiated fuel.
History
For decades, high level radioactive waste has accumulated at reactor sites and continues to do so as nuclear reactors generate more waste. Without a credible plan to permanently isolate it, storage pools, where irradiated nuclear waste is currently stored until it becomes less hot, have been tightly packed and re-racked to accommodate all the waste.
Unfortunately, the pools and dry casks have no robust containment. If the cooling pumps stopped operating or the water in the pools drained out, temperatures would quickly increase, as happened in Fukushima Japan, and could result in a similar disaster.
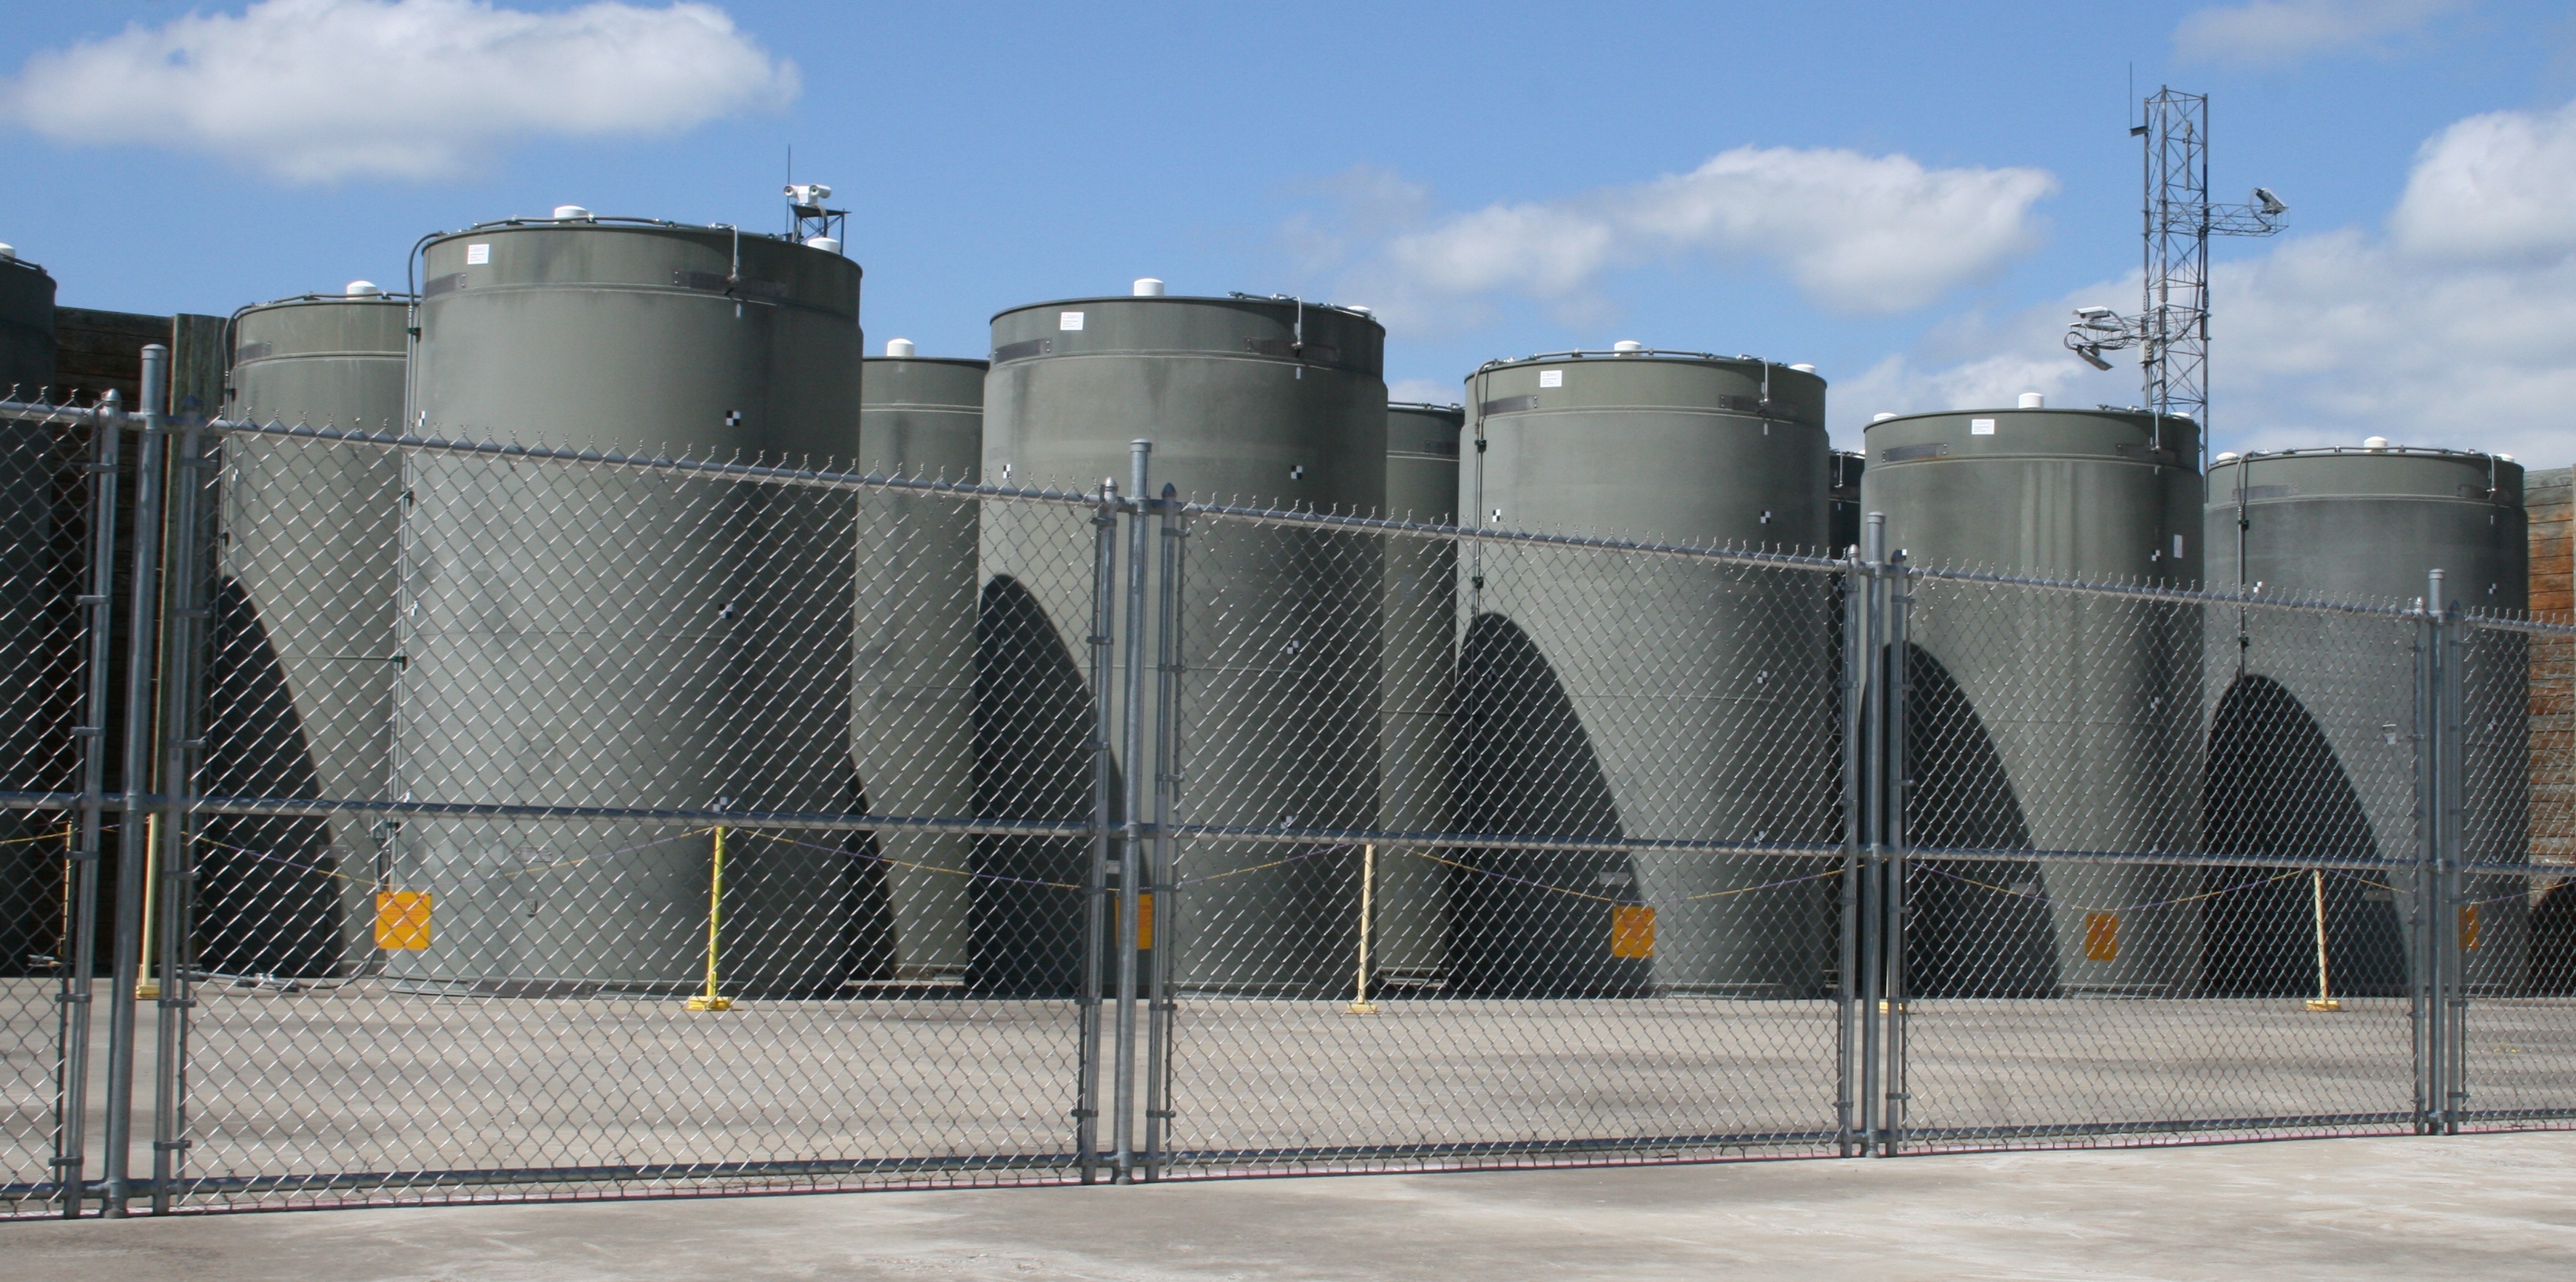
Current dry cask storage at reactor sites (pictured above) is extremely vulnerable. There is often nothing more than a chain-link fence and a short distance that separates the highly radioactive waste containers and public access.
Establishing interim hardened on-site storage (HOSS) is a top priority. Hardened on-site storage allows waste generators to store high level waste as close to the site of generation as possible, thereby exposing fewer people to radiation, as safely as possible.
Rather than storing dozens of vulnerable dry-casks next to each other in the open air, the HOSS Principles established by concerned citizens mandate:
Irradiated fuel must be stored as safely as possible as close to the site of generation as possible;
HOSS facilities must not be regarded as a permanent waste solution, and thus should not be constructed underground and the waste must be retrievable;
The facility must have real-time radiation and heat monitoring for early detection of problems with containers;
The overall objective of HOSS should be that the amount of releases projected in even severe attacks should be low enough that the storage system would be unattractive as a terrorist target;
Placement of individual canisters that makes detection difficult from outside the site boundary.
Hardened On-Site Storage (HOSS) is supported by organizations in all 50 states. The Principles of Securing Nuclear Waste at Nuclear Reactor Sites are posted here. It would provide better security at reactor sites with robust dry storage and community oversight, including real-time monitoring of heat and radiation. HOSS is rooted in values of community protection and environmental justice and will provide increased protection from human or natural disasters, like terrorist attacks and earthquakes
HOSS facilities are not permanent waste solutions, and therefore should not be constructed deep underground as the waste must be retrievable. However, they are a workable solution that will allow us to explore scientifically sound, and socially and environmentally just long-term management systems.
Nuclear Power Has No Place in a Green Energy Future
Because of: Time Delay, Success of Renewables, Huge Costs, Dangers, Weapons Connection, and Wastes
from Yahoo News, 21 Oct 21, ”…….Practical concerns also temper enthusiasm for a nuclear future. The next generation of reactors, heralded as a game changer by supporters, still haven’t been proven in the real world. Even if those technologies are as revolutionary as advertised, skeptics say it could take decades before they make a real difference in the global energy grid — too long if the worst outcomes of climate change are to be avoided.
Renewable energy technologies can be enough on their own
“The drawbacks to nuclear are compounded by the burgeoning success of renewables — both solar and wind are getting cheaper and more efficient, year after year. There is also a growing realisation that a combination of renewables, smart storage, energy efficiency and more flexible grids can now be delivered at scale and at speed — anywhere in the world.” — Jonathon Porritt, Guardian
The world doesn’t have time to wait for next-gen nuclear
“When it comes to averting the imminent effects of climate change, even the cutting edge of nuclear technology will prove to be too little, too late. Put simply, given the economic trends in existing plants and those under construction, nuclear power cannot positively impact climate change in the next ten years or more.” — Allison Macfarlane, Foreign Affairs
A major ramp-up in nuclear technologies isn’t economically feasible
“While nuclear power may have once been cheaper than wind or solar, the economics have since changed dramatically. Nuclear power plants are very expensive to build and the economics of nuclear power are getting steadily worse. By contrast, renewables continue to come down in price.” — Ian Lowe, Conversation
There’s no way to guarantee that nuclear plants will be safe
“People around the world have witnessed the Three Mile Island, Chernobyl and Fukushima accidents. It is more than enough to believe that a safe nuclear power plant is nothing but a myth.” — Jang Daul, Korea Times
More nuclear power could lead to more nuclear weapons
“Some nations — India and Pakistan, and in all probability Israel — became nuclear powers after originally seeking nuclear technology for research or to develop nuclear power. … This is important: The technology used to turn on lights or charge mobile phones shouldn’t need to involve national or international defence apparatus.” — Editorial, Nature
Nuclear waste is still a major problem
“Nuclear waste lasts for hundreds of thousands of years before they are half-decayed. Our United States government — perhaps the longest continuous government in the world — is only 232 years old. Who will be around to manage uranium wastes?” — David Ross, Courier-Journal
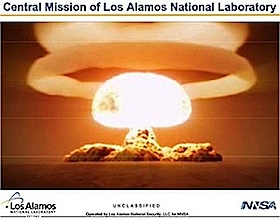
LANL’s Central Mission: Los Alamos Lab officials have recently claimed that LANL has moved away from primarily nuclear weapons to “national security”, but what truly remains as the Labs central mission? Here’s the answer from one of its own documents:
LANL’s “Central Mission”- Presented at: RPI Nuclear Data 2011 Symposium for Criticality Safety and Reactor Applications (PDF) 4/27/11
A GAO Report released Friday the 13th found that “significant information security control weaknesses remain on LANL’s classified computer network. LANL had vulnerabilities in several critical areas, including (1) identifying and authenticating the identity of users, (2) authorizing user access, (3) encrypting classified information, (4) monitoring and auditing compliance with security policies, and (5) maintaining software configuration assurance.”
The report explains that LANL spent approximately $433 million from fiscal years 2001 through 2008 to operate, maintain, protect, and procure equipment for its classified computer network. The largest expenditure for the classified computer network was for high-performance computing, which accounted for $322 million (or 74 percent) of total expenditures. LANL began to expand the classified computer network in 2005, accounting for $48 million (or 11 percent) of total expenditures during the fiscal year 2001 through fiscal year 2008 period. Expenditures for special initiatives, such as the Integrated Cyber Security Initiative and Multi-Platform Trusted Copy program, accounted for $19 million (or 4 percent) of total expenditures. The core classified cyber security program, which serves as the foundation of LANL’s protection strategy for the classified cyber security program, accounted for $45 million (or 10 percent) of total expenditures over the period.
Clearly, the Lab was more focused on high-performance computing rather than focusing on protecting the nation’s nuclear secrets, or maybe the Lab thought everything was OK.
This GAO report comes after the DOE Office of Enforcement devoted significant attention to monitoring compliance with a Secretarial Compliance Order that was issued in July 2007. Specifically, the DOE Secretary directed the contractor for the Los Alamos National Laboratory – Los Alamos National Security, LLC – to remediate deficiencies that contributed to a breach of classified information security controls and to correct longstanding deficiencies associated with classified information security, and classified and unclassified cyber security programs. Los Alamos National Laboratory reported that the actions were completed by December 2008, and the DOE Los Alamos Site Office formally validated completion of the required actions.
But problems were still not corrected. To satisfy the above July 2007 DOE Compliance Order, the laboratory reaccredited all classified computer systems. During 2008, as part of its reaccredidation process, LANL revised risk assessments for classified computer systems and included the results in the system security plans. However, of the five system security plans the GAO reviewed, one plan’s risk assessment did not adhere to the latest methodology and did not include evidence of a comprehensive threat analysis, as required by DOE. Furthermore, the remaining four plans noted that all known threats and vulnerabilities were not evaluated to determine risks. Without comprehensive risk assessments, risks to certain systems may be unknown and appropriate controls may not be in place to protect against unauthorized access to or disclosure of sensitive information, or disruption of critical systems and operations.
According to data reported by the U.S. Computer Emergency Readiness Team (US-CERT), reported attacks on U.S. government computer networks climbed 40% last year, and more infiltrators are trying to plant malicious software they could use to control or steal sensitive data. Accounts of unauthorized access to government computers and installations of hostile programs rose from a combined 3,928 incidents in 2007 to 5,488 in 2008, The latest report, issued in February 2009, represented a small sampling – just 1% of federal agencies have fully developed tracking systems – and some of the uptick in reported attacks may be due to better reporting in the last year.
Government networks are targeted by foreign nations seeking intelligence, such as China and Russia, as well as criminal groups and individuals who may want to disrupt power, communication or financial systems. Some attackers are less interested in stealing data than in undermining a system’s ability to operate by planting software that could slow critical networks in emergencies. Security industry observers expressed alarm about phishing, in which seemingly legitimate e-mails solicit sensitive information, and ‘web redirects,’ which shunt a computer to a website where it downloads malicious software. According to reports, fewer attacks are being used to take down an organization’s entire IT system. Instead, attacks now penetrate IT systems without impairing them, primarily to siphon out sensitive information without detection.
Click the image to view and download this large printable map of DOE sites, commercial reactors, nuclear waste dumps, nuclear transportation routes, surface waters near sites and transport routes, and underlying aquifers. This map was prepared by Deborah Reade for the Alliance for Nuclear Accountability.
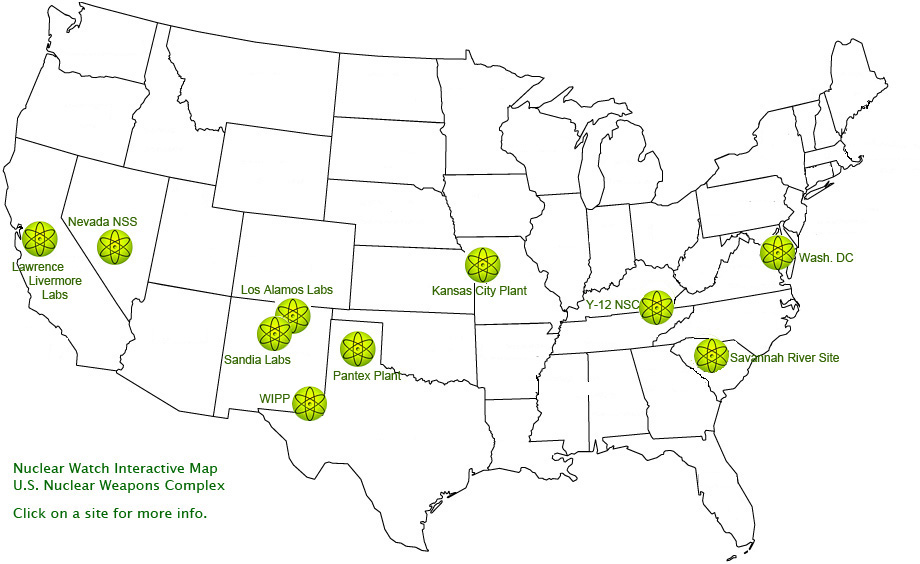
Nuclear Watch Interactive Map – U.S. Nuclear Weapons Complex
Waste Lands: America’s Forgotten Nuclear Legacy
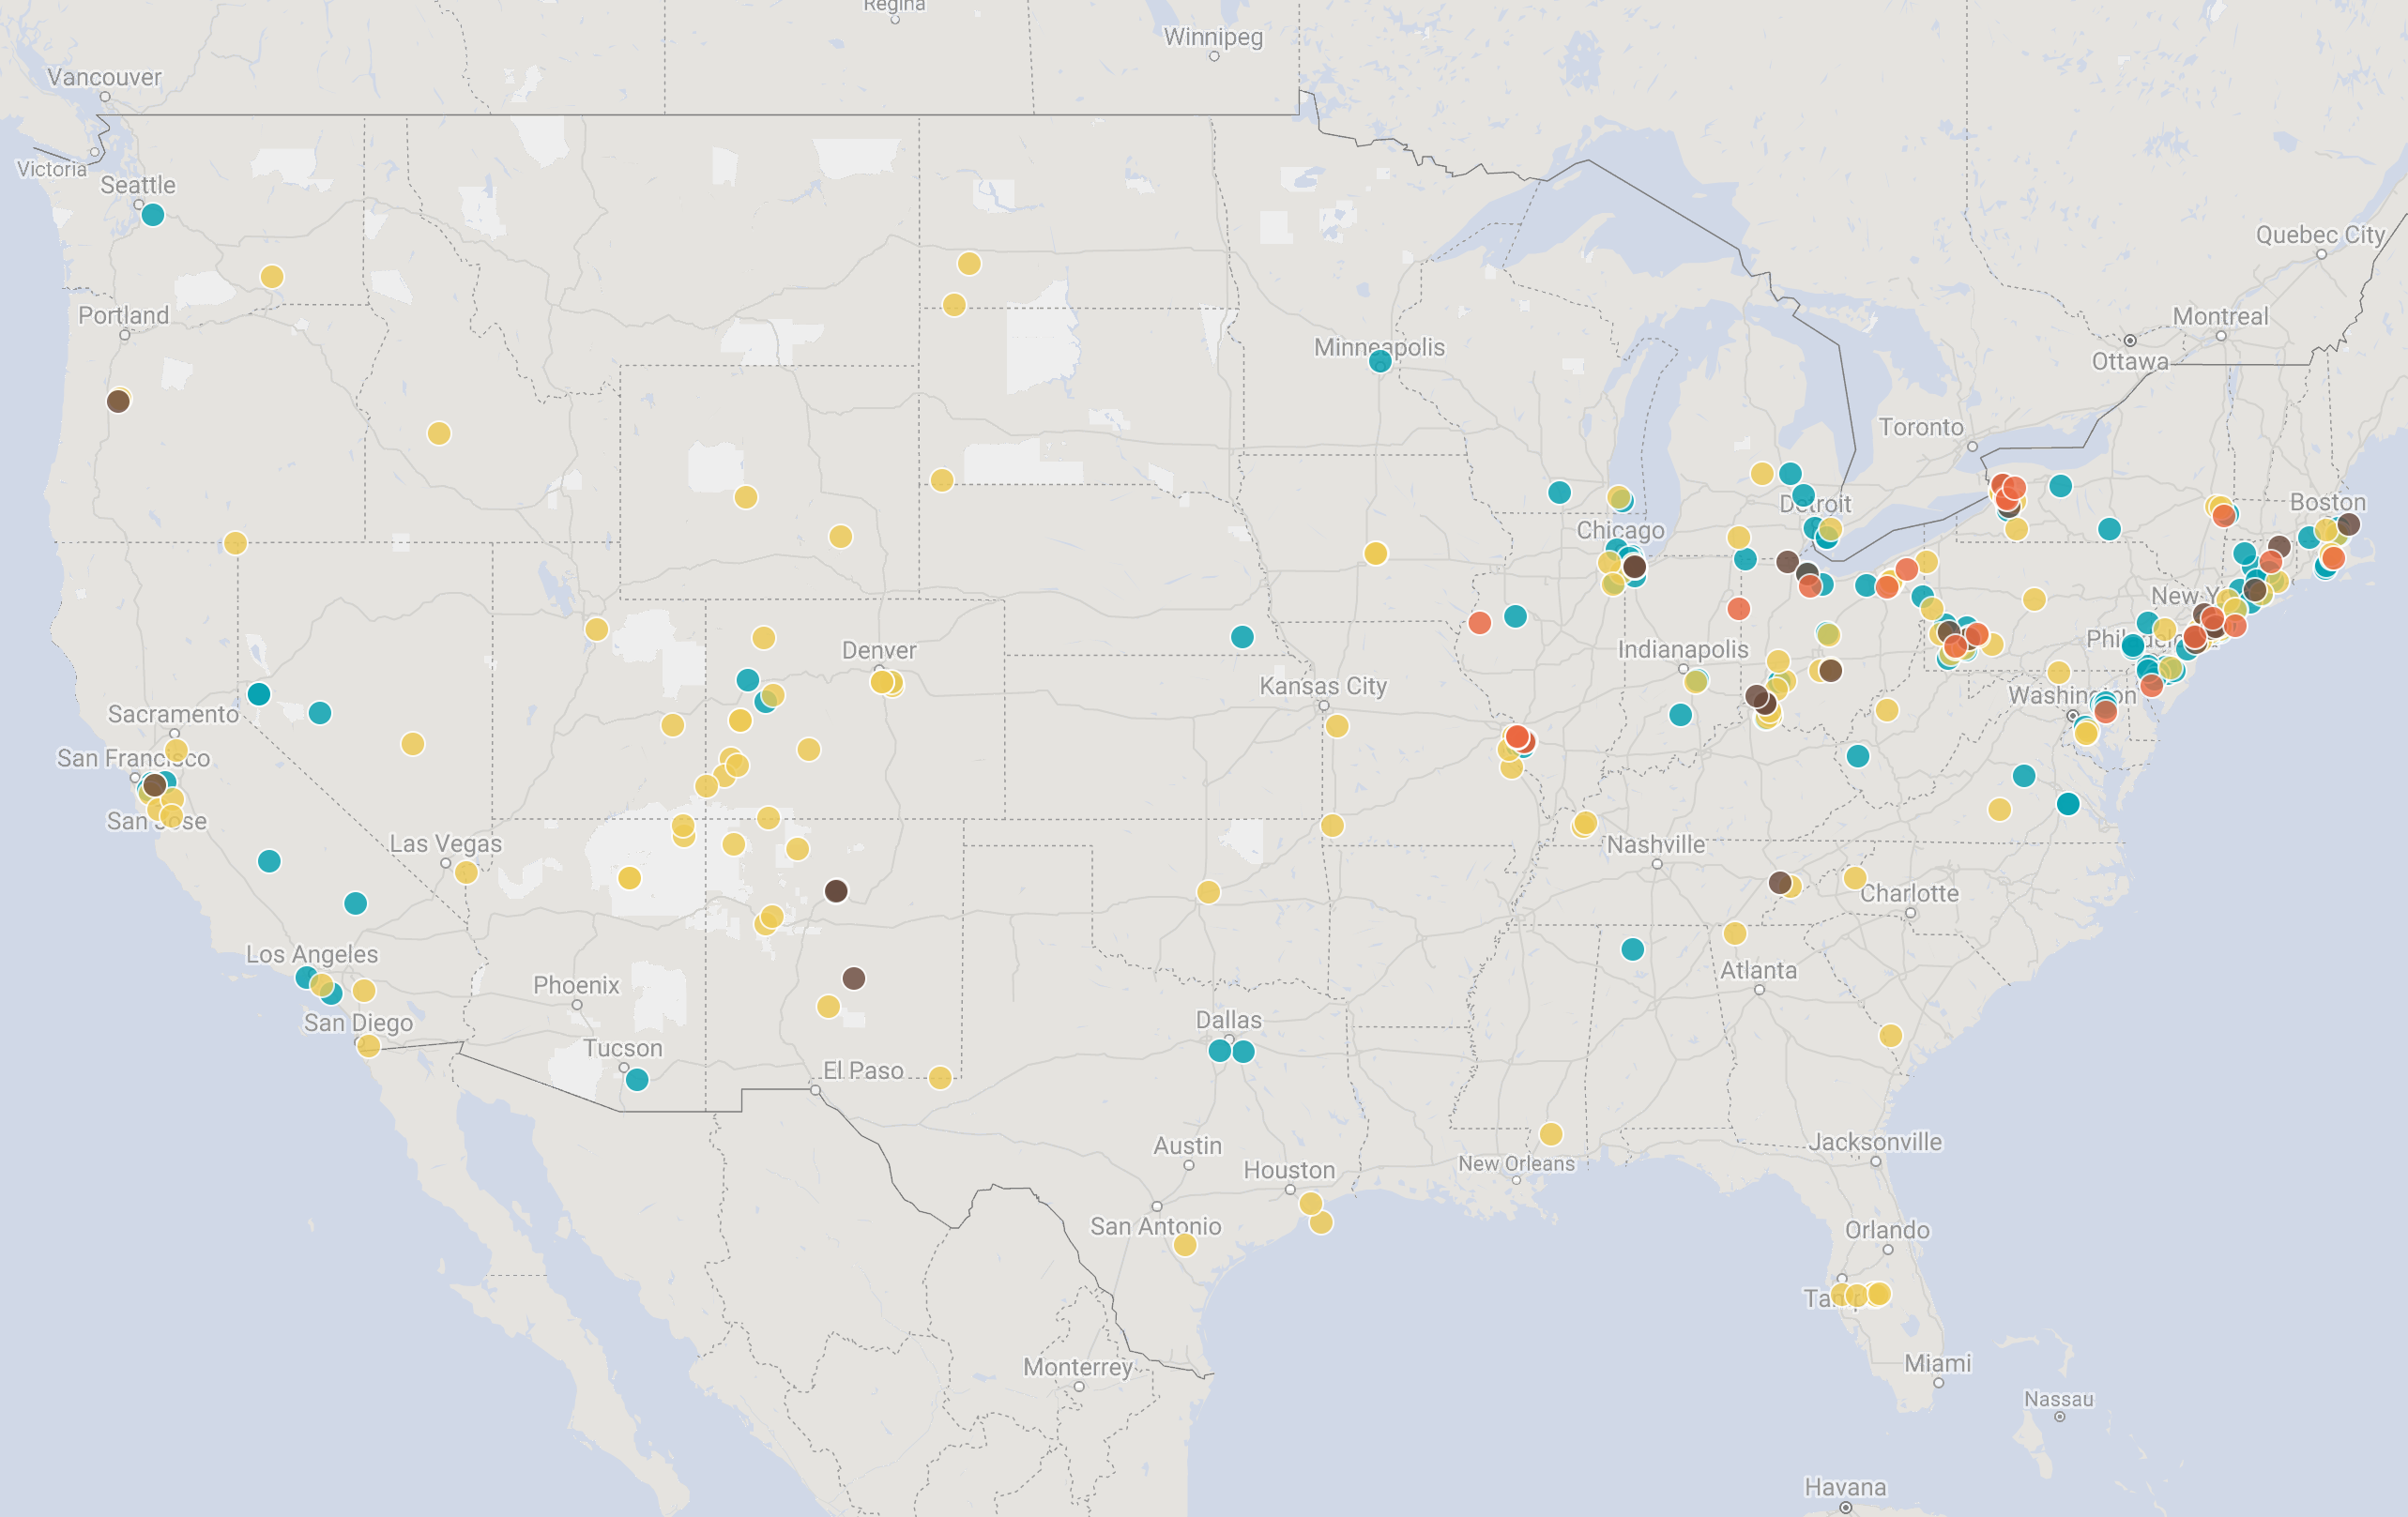
The Wall St. Journal has compiled a searchable database of contaminated sites across the US. (view)
Related WSJ report: https://www.wsj.com
A GAO Report released Friday the 13th found that “significant information security control weaknesses remain on LANL’s classified computer network. LANL had vulnerabilities in several critical areas, including (1) identifying and authenticating the identity of users, (2) authorizing user access, (3) encrypting classified information, (4) monitoring and auditing compliance with security policies, and (5) maintaining software configuration assurance.”
The report explains that LANL spent approximately $433 million from fiscal years 2001 through 2008 to operate, maintain, protect, and procure equipment for its classified computer network. The largest expenditure for the classified computer network was for high-performance computing, which accounted for $322 million (or 74 percent) of total expenditures. LANL began to expand the classified computer network in 2005, accounting for $48 million (or 11 percent) of total expenditures during the fiscal year 2001 through fiscal year 2008 period. Expenditures for special initiatives, such as the Integrated Cyber Security Initiative and Multi-Platform Trusted Copy program, accounted for $19 million (or 4 percent) of total expenditures. The core classified cyber security program, which serves as the foundation of LANL’s protection strategy for the classified cyber security program, accounted for $45 million (or 10 percent) of total expenditures over the period.
Clearly, the Lab was more focused on high-performance computing rather than focusing on protecting the nation’s nuclear secrets, or maybe the Lab thought everything was OK.
This GAO report comes after the DOE Office of Enforcement devoted significant attention to monitoring compliance with a Secretarial Compliance Order that was issued in July 2007. Specifically, the DOE Secretary directed the contractor for the Los Alamos National Laboratory – Los Alamos National Security, LLC – to remediate deficiencies that contributed to a breach of classified information security controls and to correct longstanding deficiencies associated with classified information security, and classified and unclassified cyber security programs. Los Alamos National Laboratory reported that the actions were completed by December 2008, and the DOE Los Alamos Site Office formally validated completion of the required actions.
But problems were still not corrected. To satisfy the above July 2007 DOE Compliance Order, the laboratory reaccredited all classified computer systems. During 2008, as part of its reaccredidation process, LANL revised risk assessments for classified computer systems and included the results in the system security plans. However, of the five system security plans the GAO reviewed, one plan’s risk assessment did not adhere to the latest methodology and did not include evidence of a comprehensive threat analysis, as required by DOE. Furthermore, the remaining four plans noted that all known threats and vulnerabilities were not evaluated to determine risks. Without comprehensive risk assessments, risks to certain systems may be unknown and appropriate controls may not be in place to protect against unauthorized access to or disclosure of sensitive information, or disruption of critical systems and operations.
According to data reported by the U.S. Computer Emergency Readiness Team (US-CERT), reported attacks on U.S. government computer networks climbed 40% last year, and more infiltrators are trying to plant malicious software they could use to control or steal sensitive data. Accounts of unauthorized access to government computers and installations of hostile programs rose from a combined 3,928 incidents in 2007 to 5,488 in 2008, The latest report, issued in February 2009, represented a small sampling – just 1% of federal agencies have fully developed tracking systems – and some of the uptick in reported attacks may be due to better reporting in the last year.
Government networks are targeted by foreign nations seeking intelligence, such as China and Russia, as well as criminal groups and individuals who may want to disrupt power, communication or financial systems. Some attackers are less interested in stealing data than in undermining a system’s ability to operate by planting software that could slow critical networks in emergencies. Security industry observers expressed alarm about phishing, in which seemingly legitimate e-mails solicit sensitive information, and ‘web redirects,’ which shunt a computer to a website where it downloads malicious software. According to reports, fewer attacks are being used to take down an organization’s entire IT system. Instead, attacks now penetrate IT systems without impairing them, primarily to siphon out sensitive information without detection.
Important Documents & Articles Related to Nuclear Energy Production
Most Recent
Nothing Found
It seems we can’t find what you’re looking for. Perhaps searching can help.
See Also
Nuclear Watch Interactive Map – U.S. Nuclear Weapons Complex
Waste Lands: America’s Forgotten Nuclear Legacy
The Wall St. Journal has compiled a searchable database of contaminated sites across the US. (view)
Related WSJ report: https://www.wsj.com
LANL’s Central Mission: Los Alamos Lab officials have recently claimed that LANL has moved away from primarily nuclear weapons to “national security”, but what truly remains as the Labs central mission? Here’s the answer from one of its own documents:
LANL’s “Central Mission”- Presented at: RPI Nuclear Data 2011 Symposium for Criticality Safety and Reactor Applications (PDF) 4/27/11